
블로그
전체 블로그
CertiK는 개발자와 사용자를 위해 Web3 보안, 블록체인 감사 및 규정 준수에 관한 블로그와 고객 사례 등 교육 콘텐츠를 제공합니다.
 리서치 보고서Jump Satoshi Exit ScamOn 09 October 2022 JUMPN aka Jump Satoshi, withdrew $1.1 million from their JST token by which all the project's socials, including their website had been taken down. Two days later, all contracts associated with Jump Satoshi were drained of assets in an exit scam totaling $3.9m.
 리서치 보고서Loser Coin Incident AnalysisOn May 14, 2022, loser coin ($lowb) experienced a flash loan attack, leading to approximately ~$10K USD worth of asset loss.
 리서치 보고서Space Dumpling Incident AnalysisOn May 15, 2022, the Space Dumpling token (SDUMP) was exploited, leading to a loss of 7.6 BNB around ~$2,000 at time of incident. The attacker took advantage of Space Dumpling anti-whale mechanism and drained funds from its liquidity pools. The attacker obfuscated the profits through Tornado Cash on June 1, 2022.
 기술 인사이트Formal Verification, the Move Language, and the Move ProverIn this post, we take a deep dive into the formal verification of Move programs.
 기술 인사이트Upgradeable Proxy Contract Security Best PracticesProxy patterns enable contracts to upgrade their logic while maintaining their on-chain address and state values. This article gives an overview of the types of proxy contracts, associated security incidents and recommendations, as well as best practices when implementing a proxy contract.
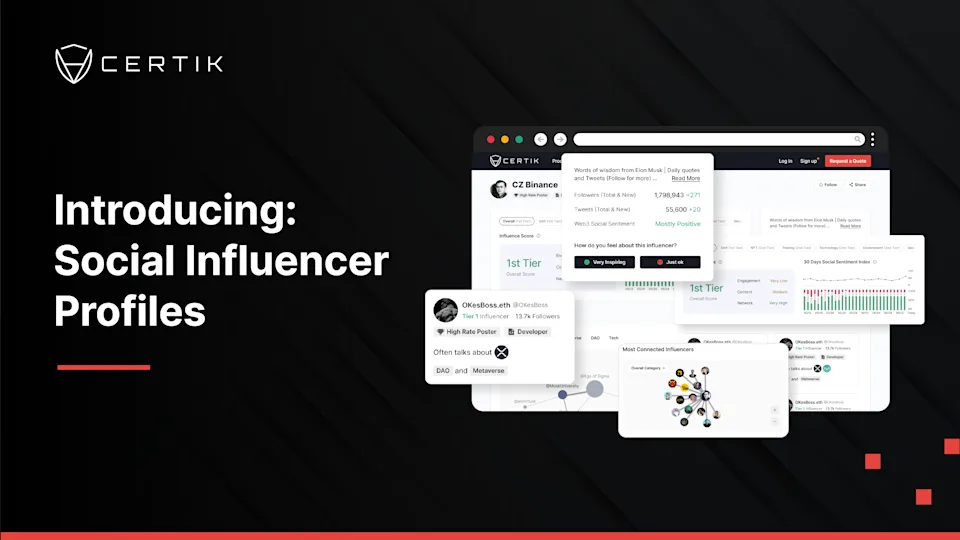 회사 소식Introducing Social Influencer ProfilesCertiK is excited to announce the release of a new due diligence tool to help you conduct social analysis: Social Influencer Profiles.
 리서치 보고서Unveiling the KYC Actor IndustryCertiK has unveiled an underground ring of KYC actors for hire, used by rogue developers to scam Web3 communities.
 리서치 보고서Novo Defi Incident AnalysisOn 29 May 2022, Novo Defi’s token, Novo, was exploited via a flash loan attack. The incident caused a loss of ~278 BNB
 리서치 보고서Hackerdao Incident AnalysisOn May 24th 2022, the Hackerdao (Hackerdao) token was exploited by flashloan attacks, causing a loss of around 200 BNB, which was around $65K at the time of incident.
 리서치 보고서Nirvana Finance Incident AnalysisOn July 28th, 2022, Nirvana Finance was exploited via flash loan attack with the attacker profiting 3.5M.
 기술 인사이트Moving the Immovables: Lessons Learned From Our Aptos Smart Contract AuditWhile auditing smart contracts written in Move, we've encountered multiple instances of developers neglecting to use Move’s built-in protection mechanisms or adopting programming patterns that work counter to Move’s design philosophy. This post presents a few such examples along with our suggestions for how to fix them.
 기술 인사이트An Introduction to MoveMove is a relatively new programming language which has seen application in a number of Web3 projects. We recently audited a novel Layer 1 blockchain which supports smart contracts written in Move, and thought we’d take this opportunity to give a general overview of Move.