
블로그
리서치 보고서
Web3 보안 현황을 다루는 심층 보안 보고서, 사고 분석 및 산업 리서치.
 보안 사고 분석The IEGT Exit Scam: A Complex Web of DeceptionOn July 22, 2023, IEGT orchestrated an exit scam, resulting in a $1.14 million loss. While not the largest fraudulent act of the year, its complexity was unparalleled, especially in the clever camouflage of team wallet balances.
 Lazarus Group's Web3 RampageSince the $650 million exploit of the Ronin bridge in 2022, attention has firmly been on North Korea’s Lazarus Group—the culprits behind the operation.
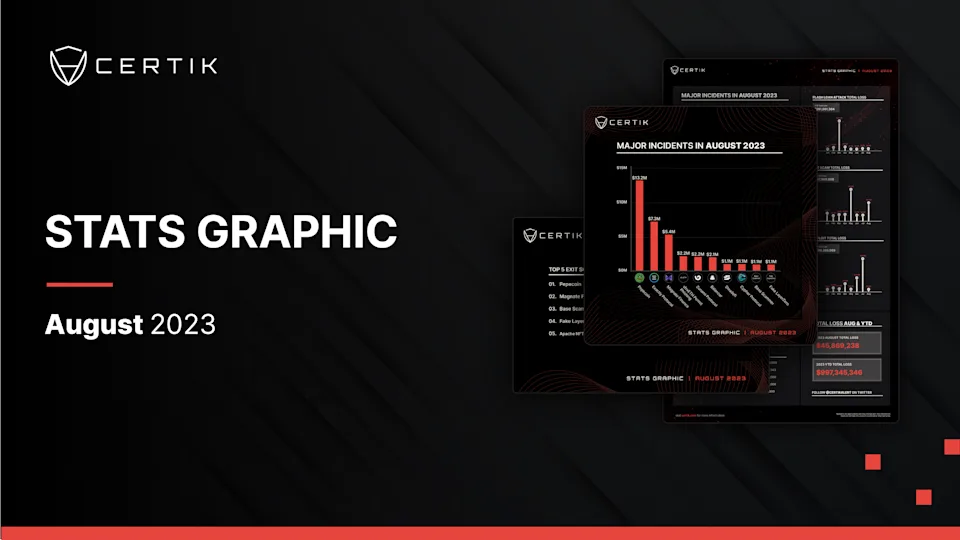 August Stats GraphThe August Stats Graphic shows data from hacks, scams, and incidents in August 2023
 산업 리서치Faint Traces: Unmasking a Million-Dollar ScammerCertiK analysts have been closely monitoring a scammer known as "Faint" since late 2022. This individual has been linked to numerous Discord compromises and phishing activities on both Ethereum and Solana.
 보안 사고 분석Zunami Protocol Incident AnalysisOn 13 August, 2023 Zunami Protocol suffered an exploit via flash loan attack, resulting in a loss of ~$2.16 million
 산업 리서치Chasing Shadows: A Decade of Criminal Crypto SeizuresAs cryptocurrency has risen in prominence over the past decade, governments worldwide have increasingly targeted illicit funds and criminal activity in the space. This pursuit has included arresting individuals involved and confiscating vast amounts of digital assets.
 July Stats GraphThe July Stats Graphic shows data from hacks, scams, and incidents in July 2023
 산업 리서치On-Chain Ransomware - The Ryuk Group: Part TwoTwo Russian cyber criminal gangs, Conti and Ryuk, dominated the ransomware scene between 2018 and 2022. Despite both groups operating within separate two year windows (Ryuk from 2018 to 2020; Conti from 2020 to 2022), our analysis has identified cryptocurrency wallets belonging to both groups that were active outside of these timelines.
 보안 사고 분석Kokomo Finance On 26 March, 2023, Kokomo Finance (KOKO) on the Optimism Smart Chainconducted an exit scam and stole ~$4 million in user funds.
 보안 사고 분석Vyper Incident AnalysisOn July 30, reports surfaced of vulnerabilities in Vyper versions 0.2.15, 0.2.16 and 0.3.0 which left many Curve pools vulnerable to a reentrancy attack.
 보안 사고 분석Conic Finance Incident AnalysisOn 21 July, 2023 the Conic Finance ETH Omnipool was exploited for 1724 ETH (\$3.2 million) via a read-only reentrancy vulnerability. Despite having reentrancy guards in place, an incorrect assumption led to a reentrancy guard being bypassed. Conic paused the ETH Omnipool but a few hours later they lost a further \$300,000 to MEV arbitrage in the crvUSD Omnipool.
 보안 사고 분석Palmswap Incident AnalysisOn 24 July, 2023 Palmswap fell victim to a flash loan exploit, resulting in the loss of 901,455 USDT.