
블로그
전체 블로그
CertiK는 개발자와 사용자를 위해 Web3 보안, 블록체인 감사 및 규정 준수에 관한 블로그와 고객 사례 등 교육 콘텐츠를 제공합니다.
 리서치 보고서Mobius Token Incident AnalysisOn 11 May 2025, our system detected a suspicious attack involving Mobius Token #MBU on Binance Smart Chain #BSC, which resulted in an approximate loss of $2.16M
 회사 소식컨센서스 2025의 CertiK: 참석자 가이드웹 3.0 보안 선도 기업이자 이번 컨퍼런스의 중요한 후원사인 CertiK는 전 세계의 웹 3.0 참가자들을 진심으로 초대하여 당사의 최첨단 보안 연구에 대해 자세히 알아보고, 웹 3.0의 미래에 대해 논의하고, 업계 보안을 촉진할 수 있는 기회를 마련하고자 합니다. 이 가이드는 컨센서스 2025에서 CertiK의 흥미진진한 활동을 안내하고 당사와의 대화형 일정을 효율적으로 계획하는 데 도움이 될 것입니다.
 기술 인사이트PancakeSwap Infinity: Hooks Security ConsiderationsThis article discusses some of the new features of PancakeSwap Infinity, and explores the security considerations related to PancakeSwap Infinity hooks.
 기술 인사이트Pectra’s EIP-7702: Redefining Trust Assumptions of Externally Owned Accounts (EOAs) in EVMIn this post, we examine how EIP-7702 reshapes core EVM assumptions, spotlight mocked examples, and provide actionable guidance for developers to assess whether their existing contracts may be vulnerable.
 기술 인사이트Oracle Wars: The Rise of Price Manipulation AttacksIn this article, we look at how oracles work, why they matter, how they can be exploited, and more, with the goal of educating DeFi participants on how to better protect themselves from these types of threats.
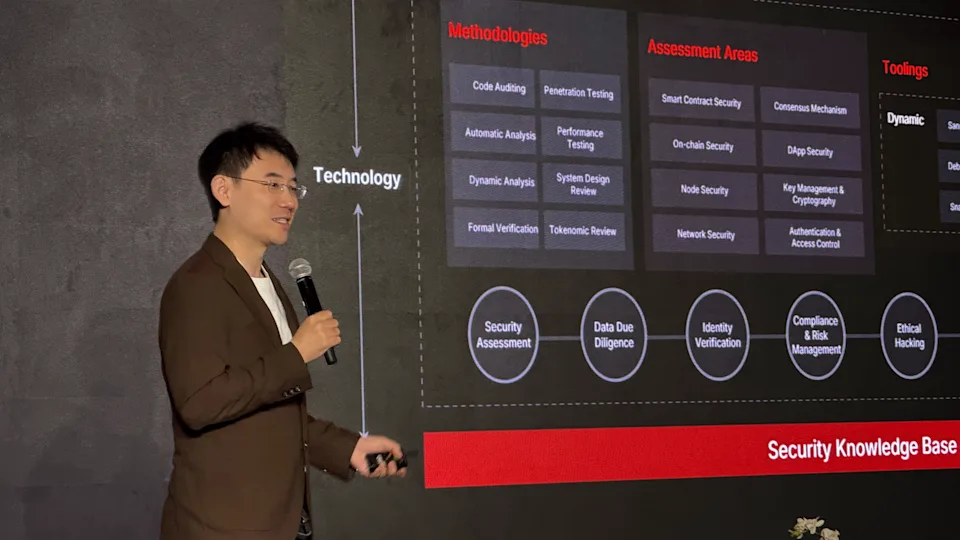 정책 동향CertiK Co-founder Ronghui Gu Speaks at Unchained Summit on Web3 Security and ComplianceRonghui Gu, Co-founder of CertiK and Associate Professor of Computer Science at Columbia University, delivered a Keynote speech at Unchained Summit Dubai 2025, emphasizing the important balance between Web3 innovation and security.
 기술 인사이트EVM – Cosmos Convergence Research From Security Base: Part 1Ethereum and Cosmos, two prominent blockchain protocols, have long pursued integration through solutions like EVM compatible chains built on Cosmos SDK (e.g. evmos/Ethermint), followed by the emerging consensus-layer (CL) swaps (e.g. Tendermint replacement for Ethereum PoS) in EVM compatible chains. This series unpacks their technical approaches and associated security trade-offs, providing an in-depth exploration of the convergence of these ecosystems.
 기술 인사이트Move for Solidity Developers I: Storage and Access Control“Move for Solidity Developers” is a series created for experienced Solidity developers who already know a bit about Move. It helps you shift from writing Solidity contracts to developing on Move-based blockchains, such as Aptos and Sui. In this first installment, we’ll explore how Move’s approach to state storage and access control differs from the Solidity/EVM model. By drawing comparisons and analogies, we aim to make these new concepts feel familiar.
 기술 인사이트A “Long Overdue” innovation in Cardano: Interoperable Programmable Token DesignAs CIP-113 advances toward finalization, CertiK is closely tracking its progress—a milestone that could reshape how developers build and enterprises engage with Cardano. This article explores the specification in depth, covering its background, the problems it addresses, its implementation, its impact on the Cardano ecosystem, comparisons with ERC-20, and security considerations.
 리서치 보고서Magic Internet Money Incident AnalysisOn 25 March 2025, MIM Spell was exploited for 6,261.13 ETH (~$12.9M) due to a vulnerability in the integration of the RouterOrder and Cauldron contracts. The attacker was able to borrow funds, liquidate themselves then borrow funds again without repaying them. This was due to the liquidation process not overwriting records in RouterOrder that counted as collateral, allowing exploiter to falsely borrow additional funds after liquidation.
 리서치 보고서0xInfini Incident AnalysisOn 24 February 2025, 0xInfini was targeted by an attack that resulted in a loss of ~$49M. A key wallet used in the attack had previously been involved in the development of Infini contracts and had retained admin rights which were used to redeem all Vault tokens.
 리서치 보고서바이비트 사건 분석2025년 2월 21일 오후 2시 16분 11초(UTC), 악의적인 컨트랙트 업그레이드로 인해 Bybit의 이더리움 콜드월렛에서 자금이 유출되었습니다. 이번 공격으로 약 14.6억 달러의 피해가 발생한 것으로 추정되며, 이는 Web3 역사상 최대 규모의 보안 사건으로 기록되었습니다.