On 24 February 2025, 0xInfini (opens in a new tab) was targeted by an attack that resulted in a loss of ~$49M. A key wallet used in the attack had previously been involved in the development of Infini contracts and had retained admin rights which were used to redeem all Vault tokens.
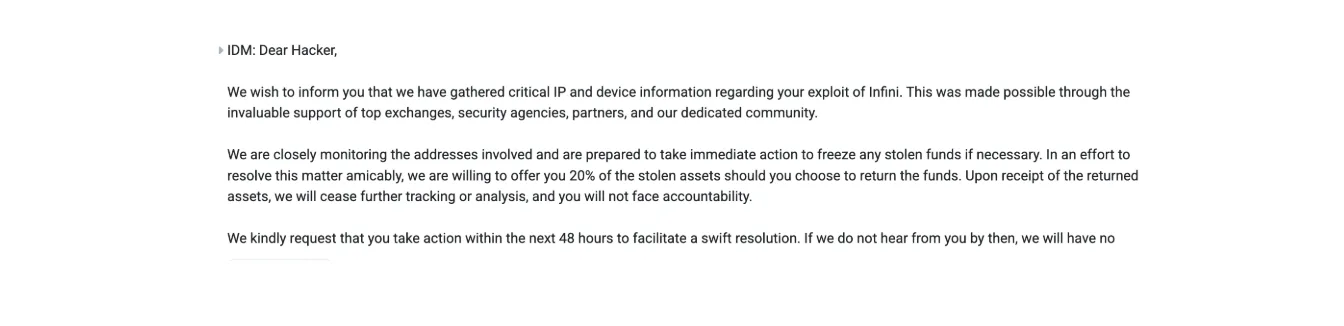
The 0xInfini team have reached out (opens in a new tab) to the attacker and offered 20% bounty as reward with a 48 hour deadline to return the remaining 80%.
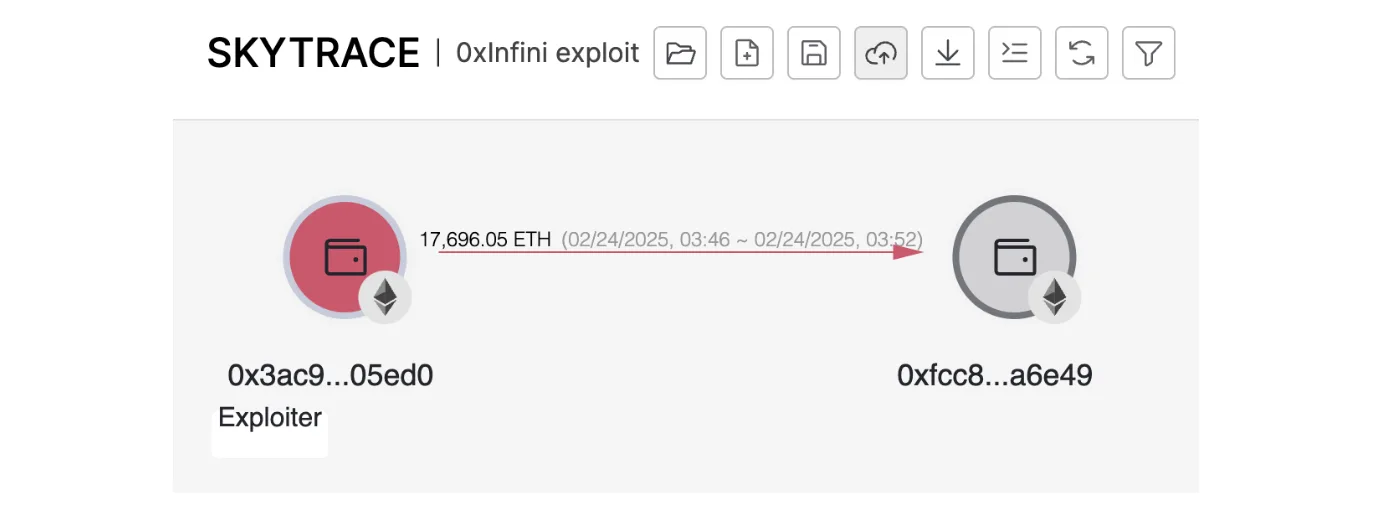
As of 27 February 2025, the stolen funds have not been returned and remain in the attacker’s wallet 0xfcC8Ad911976d752890f2140D9F4edd2c64a6e49.
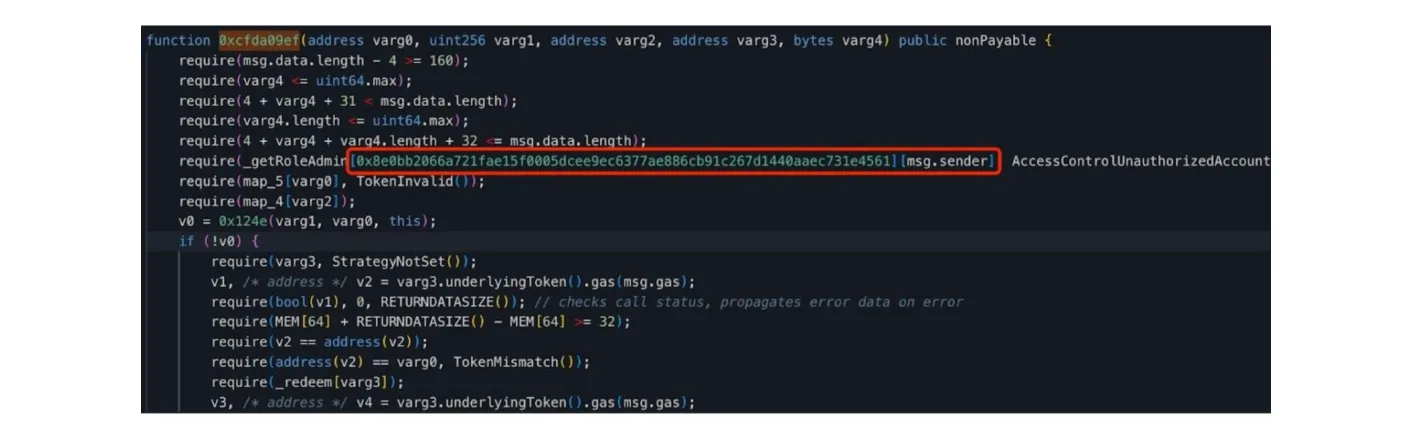
Using existing permissions, the attacker (0xc49b5e5B9DA66B9126c1a62e9761E6b2147DE3E1) was able to grant role (opens in a new tab) “0x8e0b“, which is exclusively used for function 0xcfda09ef(), to itself.
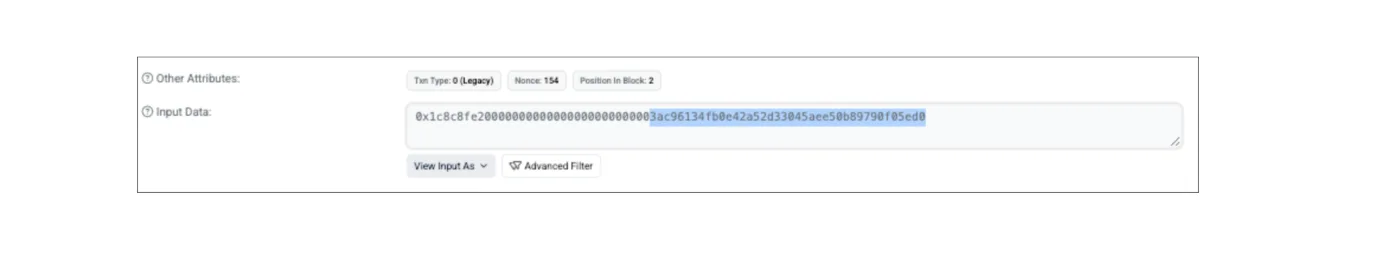
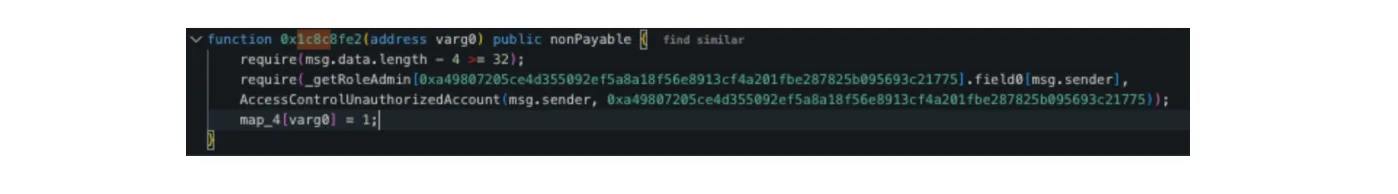
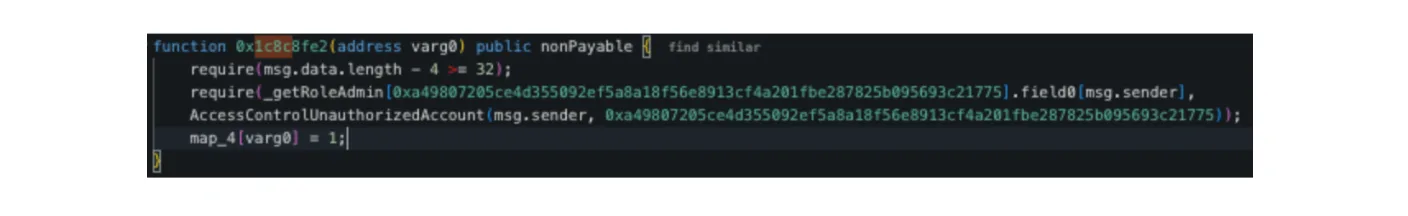
With this role the attacker executed 0x1c8c8fe2() (opens in a new tab) with 0x3ac96134fb0e42a52d33045aee50b89790f05ed0 as the input (varg0) to add the address to an allowlist.
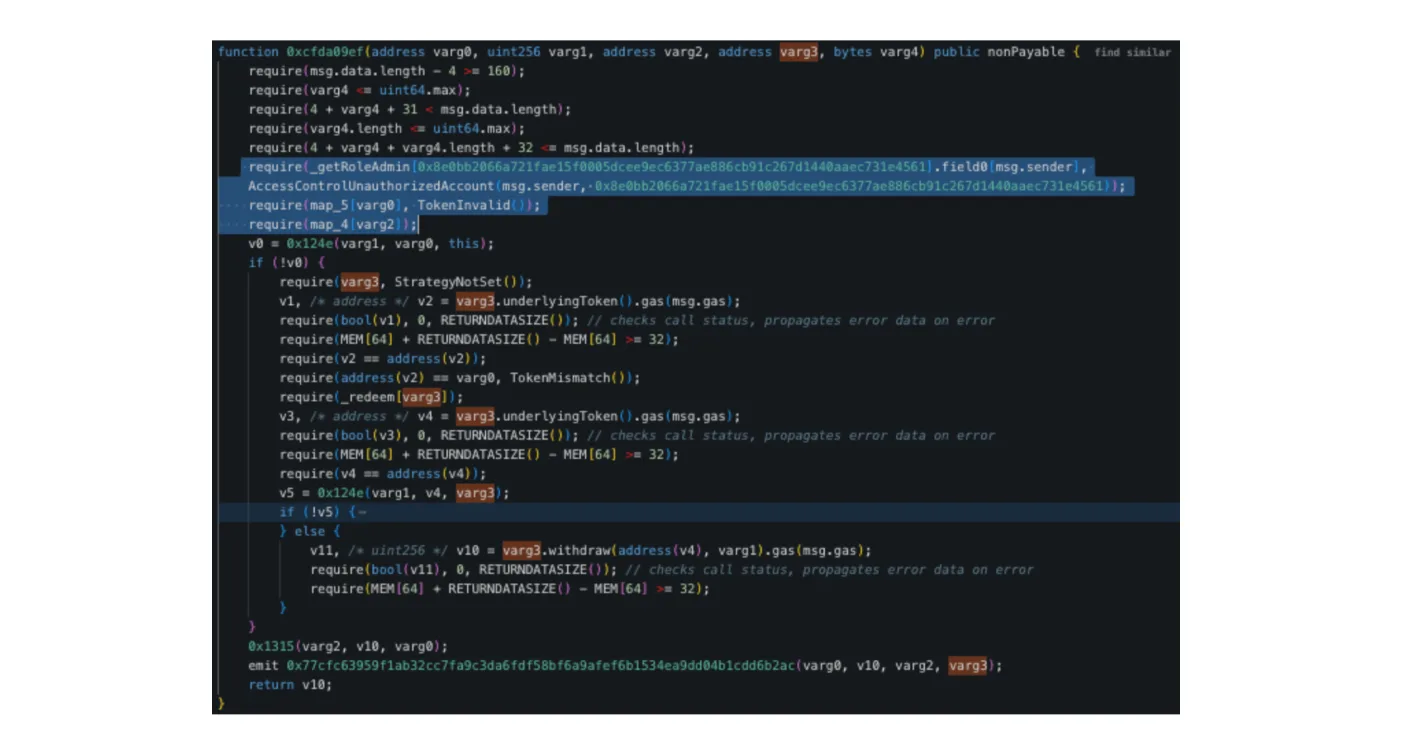
This enables the attacker to call 0xcfda09ef() and redeem all vault tokens to 0x3ac.
The compromised smart contract includes a dedicated method, 0xcfda09ef(), designed to process "vault tokens" such as resolvUSDC and USUALUSDC+. This method accepts five arbitrary inputs, among which:
varg0 represents the amount to be redeemed,
varg2 specifies the recipient address,
varg3 corresponds to the InfiniMorphoStrategy contract, responsible for managing interactions with MorphoBlue protocols and handling the vault tokens.
Besides the 0x8e0b role, the method only checks that the receiver address is listed, the token address is valid, and the strategy address is valid without requiring any additional permissions or conditions.
With the admin role it’s easy to list the receiver address by calling 0x1c8c(), effectively making the admin address a single point of failure as we have seen in this incident.
Fund Flow
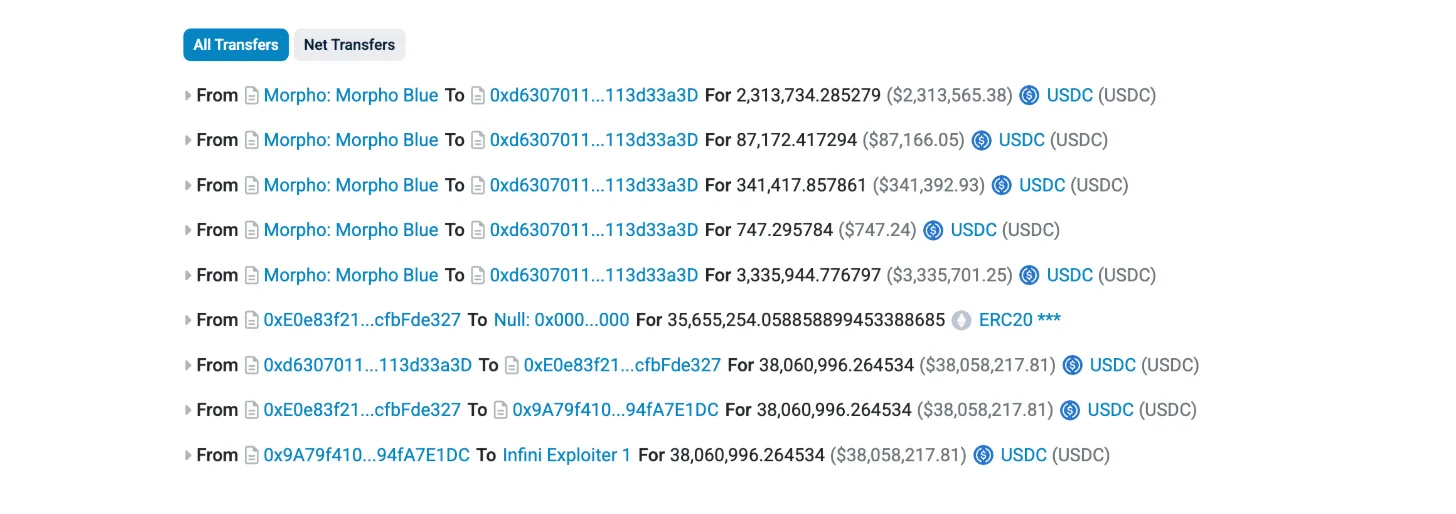
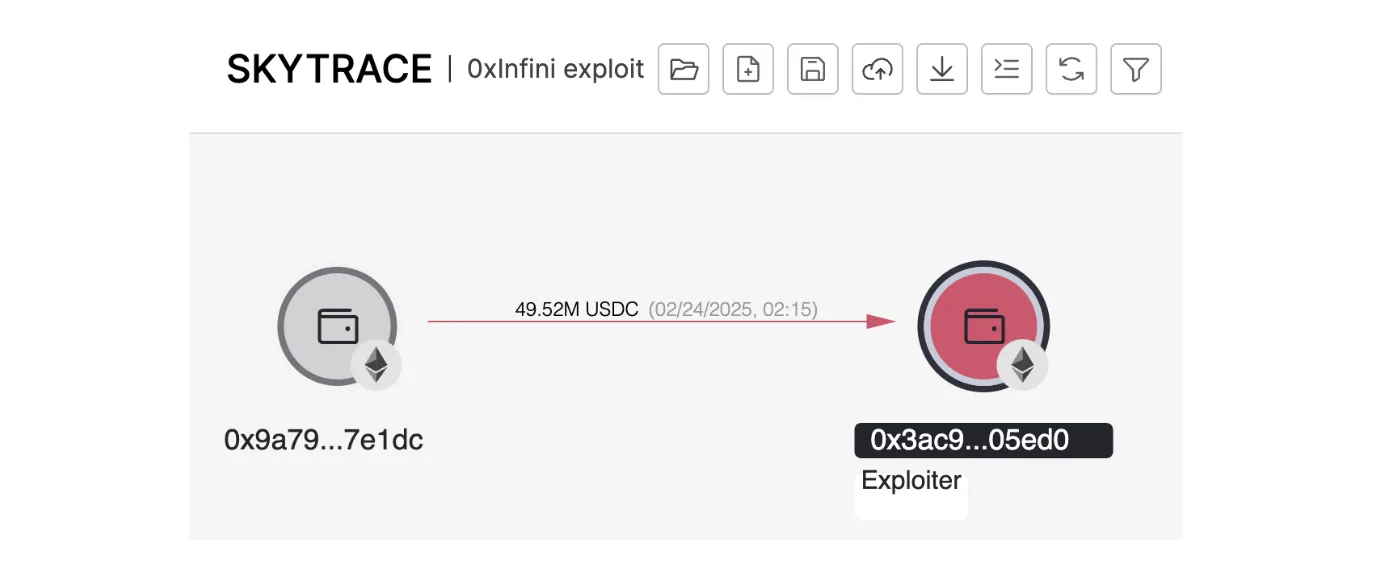
0x3ac96134fb0e42a52d33045aee50b89790f05ed0 was initially funded (opens in a new tab) from Tornado Cash a few hours before the attack with part of the ETH sent to 0xc49b5e5b9da66b9126c1a62e9761e6b2147de3e1 to cover gas fees. 0x3ac9 then received ~$49.5M USDC from the exploit.
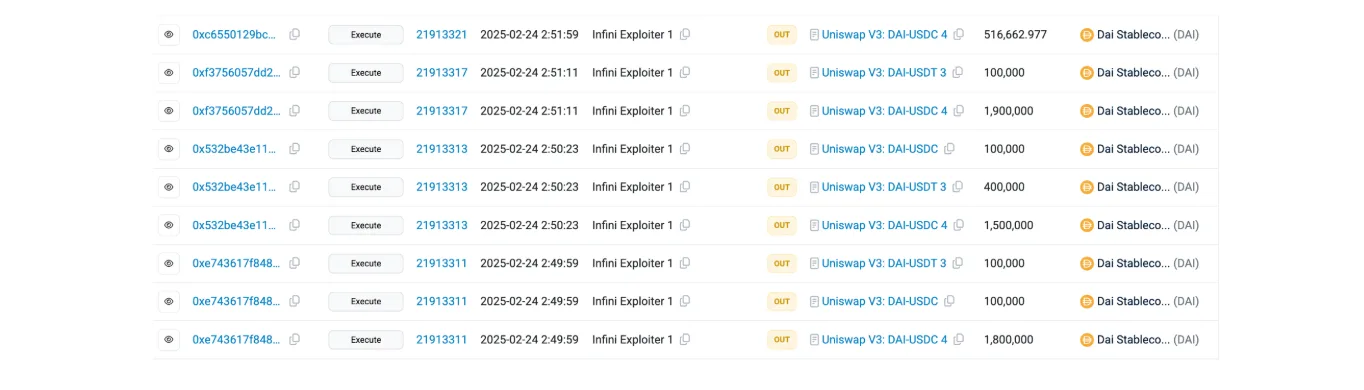
The attacker then converted the DAI into 17,696 ETH before transferring it to 0xfcc8ad911976d752890f2140d9f4edd2c64a6e49, where it still remains as of the writing.
Conclusion
The exploit highlights a major vulnerability, demonstrating how admin privileges can become a single point of failure. One fundamental aspect of blockchain security is understanding how to protect your private keys. To gain deeper insights into this foundational security principle and its implications for protecting assets, you can explore this article.