Incident Summary
On December 29, 2024 at 5:00 AM UTC, the FEG token bridge system was exploited, which permitted the attacker to withdraw FEG tokens from the bridge contract without depositing them in the source chain. The total profit for the attacker across three blockchains (Ethereum, Base, and BSC) is approximately $1 million USD.
The FEG token bridge relies on the Wormhole infrastructure to send and receive cross-chain messages. The root cause of the vulnerability was an error in the FEG cross-chain message verification process, which is unrelated to the Wormhole protocol.
Exploit Transactions
Withdraw transactions
- Ethereum: https://etherscan.io/tx/0x6c3cf48e9c8b22f60fc2b702b03f93926ee8624639b100fe851b757947e61759 (opens in a new tab)
- Base: https://basescan.org/tx/0x60fd436dbd0e99c7585b775095048eced56bfc11e18331cfcb0cdad6f9fe7d87 (opens in a new tab)
- BSC: https://bscscan.com/tx/0x3de4f3584203d7545b252df73a3b7e75db691a2c12467de42028552ca3bbf04f (opens in a new tab)
End-to-end exploit full flow (using BSC as an example)
- Initial message and transactions to add the attack contract to the FEG relayer's whitelist:
- https://basescan.org/tx/0x08b06e5b5906308a6fa64e2bc965189ea4c6e3338d0037e1ba2b9b3db88dd6c0 (opens in a new tab)
- https://bscscan.com/tx/0x7e448bbf1566c20b6973d2cbdb49092d5c6fca90ad7f1a1fc4b102e8095899d2 (opens in a new tab)
- Second message to increase the balance in the FEG bridge contract, enabling the attacker to withdraw:
- https://basescan.org/tx/0xfe6403f83c524a336623492ee0c3b4c574c42fe8b2d7b7a854c33c286317f02e (opens in a new tab)
- https://bscscan.com/tx/0x8d57aacd101b585ed5e68f9f5f79bea2082ec03862456615d9175d6c967289e4 (opens in a new tab)
- Bridge withdrawal transaction:
Addresses
Attacker
"0xCB96ddE53F43035f7395D8DbdB652987F7630b3c" on three blockchains (Ethereum, Base, and BSC)."
Smart contract addresses
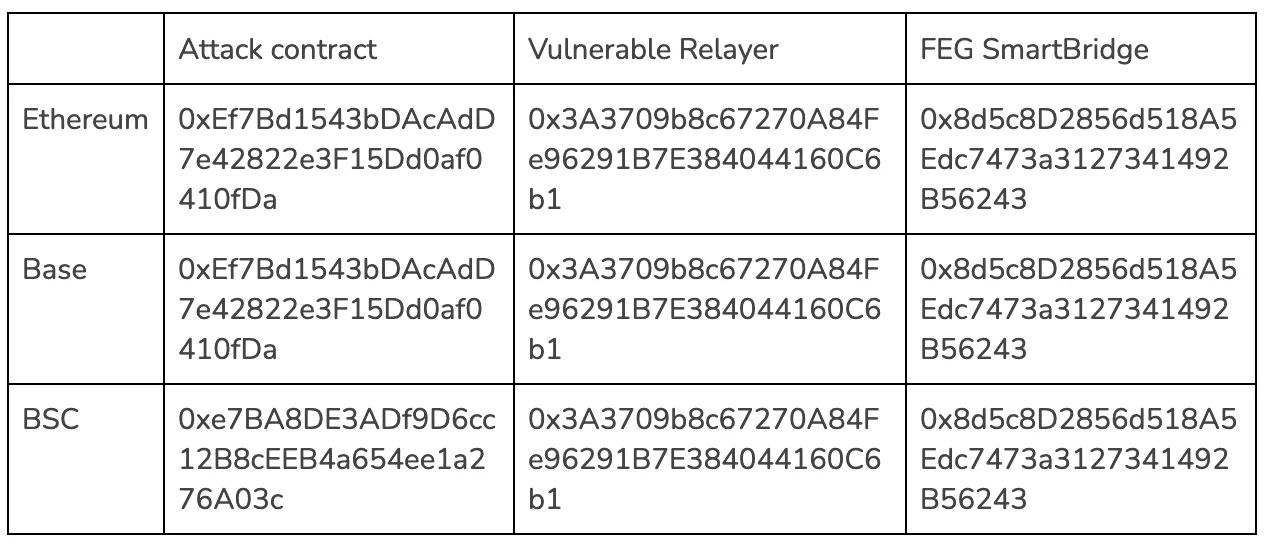
Attack Flow
Take the withdrawal on BSC as an example:
- The attacker published two messages from the source chain (Base) to the destination Chain (BSC). The first message and transactions adds the attack contract to the FEG relayer's whitelist. The second message instructs the contract on the BSC chain to perform the "registerWithdraw" function call.
Message_01
- https://basescan.org/tx/0x08b06e5b5906308a6fa64e2bc965189ea4c6e3338d0037e1ba2b9b3db88dd6c0 (opens in a new tab)
- https://bscscan.com/tx/0x7e448bbf1566c20b6973d2cbdb49092d5c6fca90ad7f1a1fc4b102e8095899d2 (opens in a new tab)
Purpose: add 0xe7ba8de3adf9d6cc12b8ceeb4a654ee1a276a03c (attack contract) to the whitelist of FEG relayer.
- sourceAddress: 0xe7ba8de3adf9d6cc12b8ceeb4a654ee1a276a03c (attack contract)
- payload:
- User = 0xbcd824fbd11ad363de83e36408a4fa47cccf2810 (FEG datareader admin), purpose: bypass the admin check
- Amount = 0
Message_02
- https://basescan.org/tx/0xfe6403f83c524a336623492ee0c3b4c574c42fe8b2d7b7a854c33c286317f02e (opens in a new tab)
- https://bscscan.com/tx/0x8d57aacd101b585ed5e68f9f5f79bea2082ec03862456615d9175d6c967289e4 (opens in a new tab)
Purpose: malicious message, set withdrawable token amount to 45,715,693,242 FEG Tokens.
- sourceAddress: 0xe7ba8de3adf9d6cc12b8ceeb4a654ee1a276a03c (attack contract)
- payload:
- User = 0xe7ba8de3adf9d6cc12b8ceeb4a654ee1a276a03c (attack contract, token receiver)
- Amount = 45,715,693,242 FEG Tokens
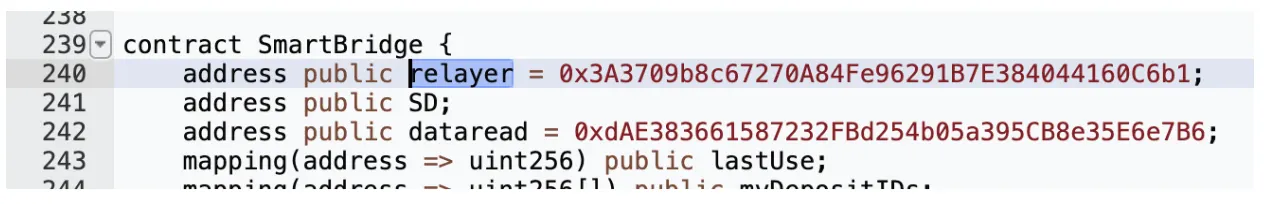
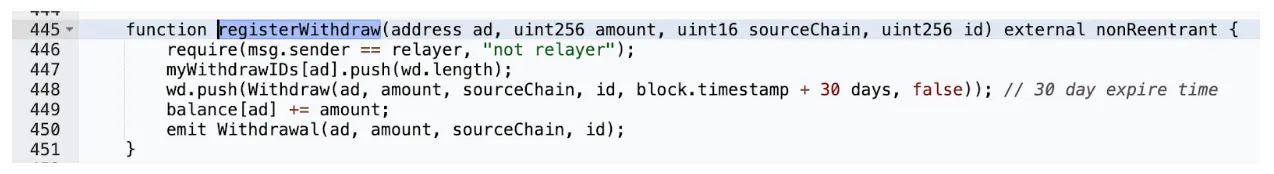
The FEG Relayer "0x3a3709b8c67270a84fe96291b7e384044160c6b1 (opens in a new tab)" received the wormhole message, processed the message, and called "registerWithdraw" in the "SmartBridge (opens in a new tab)" contract, thus registering a withdrawal balance for the attacker's contract to perform the withdrawal at a later time.
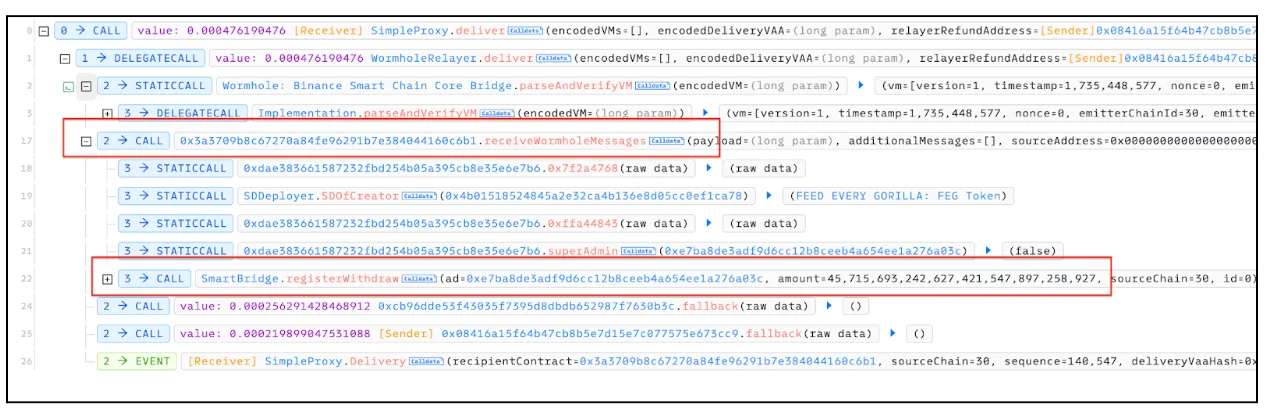
- The attacker withdrew the FEG tokens from the bridge and exchanged them for BNB: https://bscscan.com/tx/0x3de4f3584203d7545b252df73a3b7e75db691a2c12467de42028552ca3bbf04f (opens in a new tab)
Vulnerability
Take the attack on BSC as an example:
Based on the current investigation, the vulnerability is most likely located within the FEG Relayer contract "0x3A3709b8c67270A84Fe96291B7E384044160C6b1 (opens in a new tab)" of the FEG SmartBridge (opens in a new tab). The relayer contract is unverified, and the analysis is based on the decompiled code.
The FEG relayer maintains a whitelist for "sourceAddress" to reject malicious messages, which is the intended behavior. However, the relayer contains logic that allows this whitelist to be updated via a bridged message. If the "user" in the message payload is designated as the admin address, the relayer updates the whitelist to include the "sourceAddress" without verifying if the address can be trusted. The reason for including such a feature in the FEG relayer is unknown.
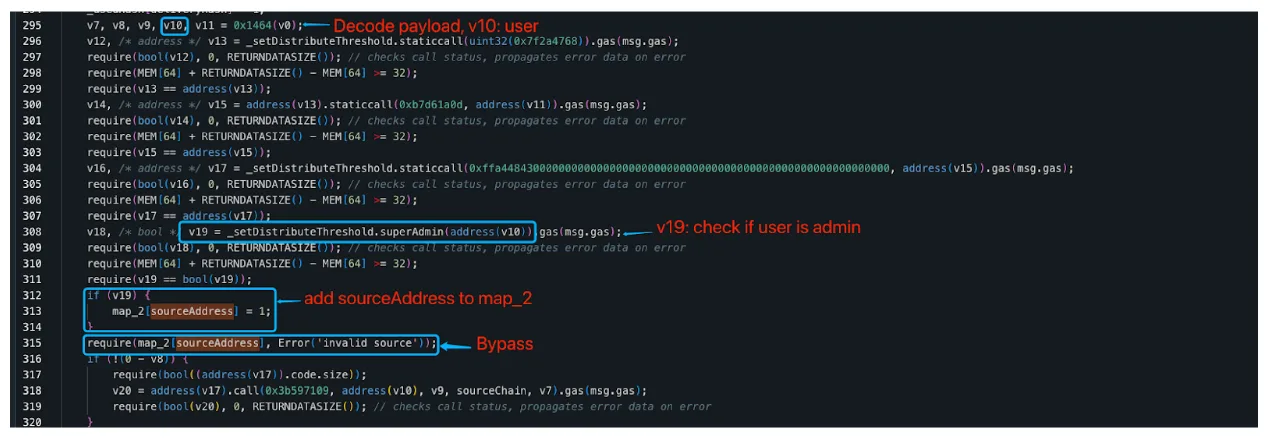
The attacker is able to add attack contract to the whitelist through the following methods:
- Send a message with payload {user = admin}, sourceAddress = attack contract.
- The FEG relayer contract adds the attack contract to the whitelist, without verifying if the "sourceAddress" can be trusted.
- After the attack contract is added to the whitelist, checking the whitelist becomes ineffective.
After the address of the attacker controlled contract is added to the whitelisted "sourceAddress", the attacker can send a malicious message to invoke the "registerWithdraw" and set the FEG balance in the FEG SmartBridge (opens in a new tab) to be withdrawable by the attacker.
Note that the relayer contract is deployed by "0x46B6dF78388284088e07aA8F5dda4B5A3Ef3f861 (opens in a new tab)," funded by "0xb44a872e035714aa057158ae2ffbbe467f13f5dd (opens in a new tab)," which received its initial funds from "FEG: Deployer 1. (opens in a new tab)" This suggests that the relayer is associated with the FEG team.
Profit and Assets Tracing
The attacker swapped the FEG tokens withdrawn from the bridge into chain-native tokens, such as ETH and BNB, during the exploit transaction. The total profit for the attacker is approximately $1 million USD. Those tokens have been sent to TornadoCash.
- Ethereum: 96.3 ETH
- Base: 73.3 ETH
- BSC: 712 BNB