On 15 July 2025, a malicious actor took advantage of a lack of input validation in Arcadia Finance (opens in a new tab)’s Rebalancer contract to obtain assets by paying off a portion of a user’s debt and withdrawing the underlying assets for a net gain of ~$3.6M.
The root cause is due to the exploiter crafting arbitrary swapData. The stolen funds are currently held on Ethereum.
Vulnerability
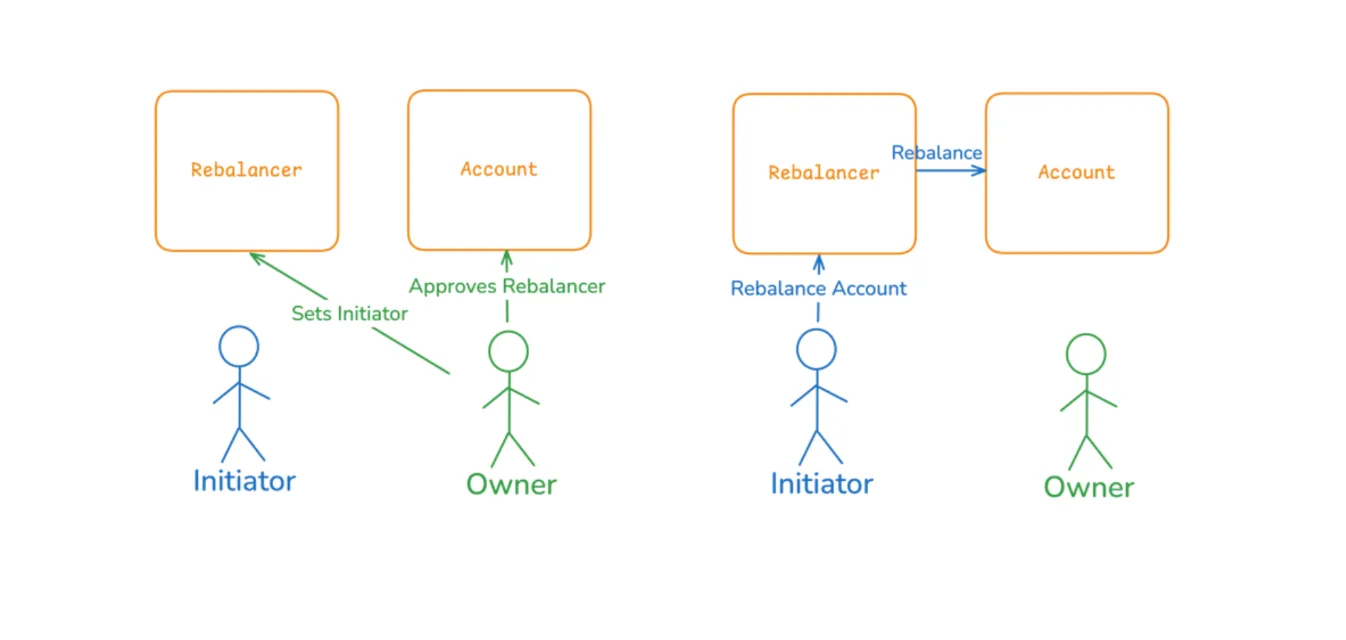
Rebalancers manage concentrated liquidity positions dynamically, solving the challenge of maintaining optimal liquidity ranges in rapidly changing market conditions.
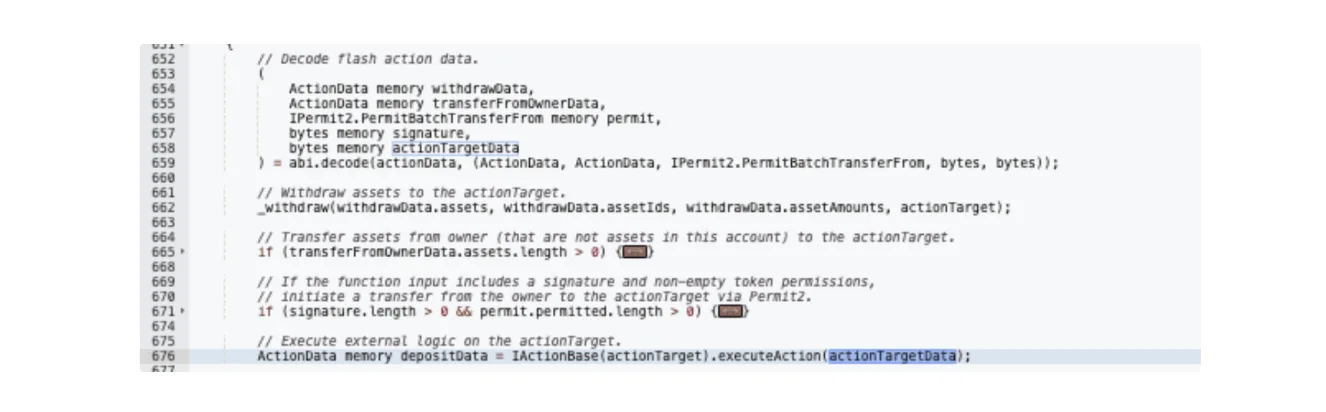
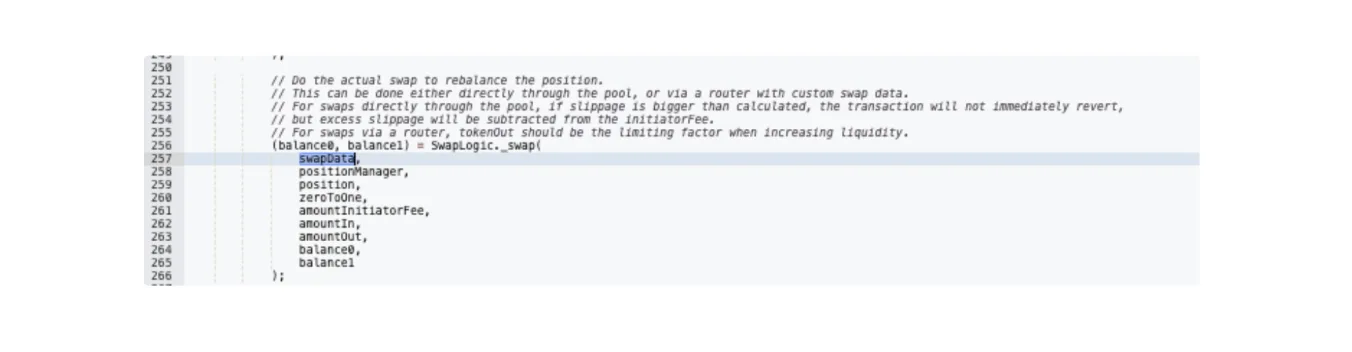
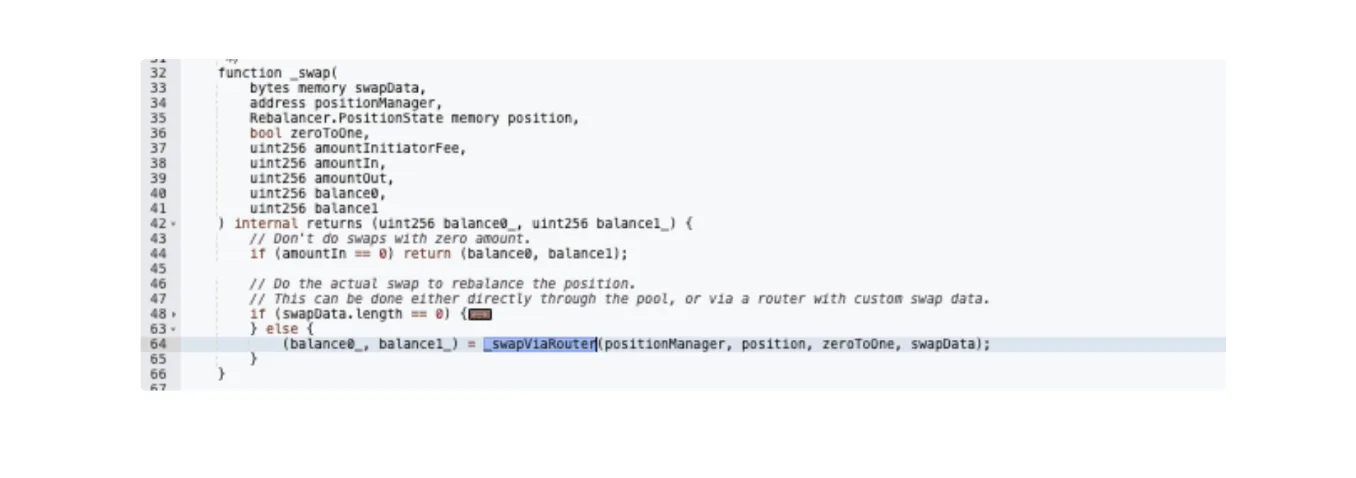
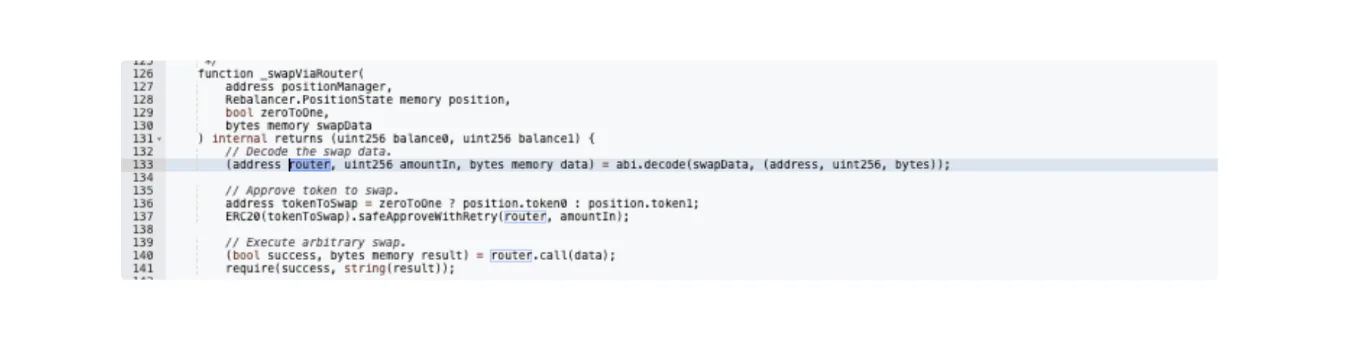
Nowhere in the above call chain are the parameters that are decoded from swapData, in particular actionTarget and router addresses, examined.
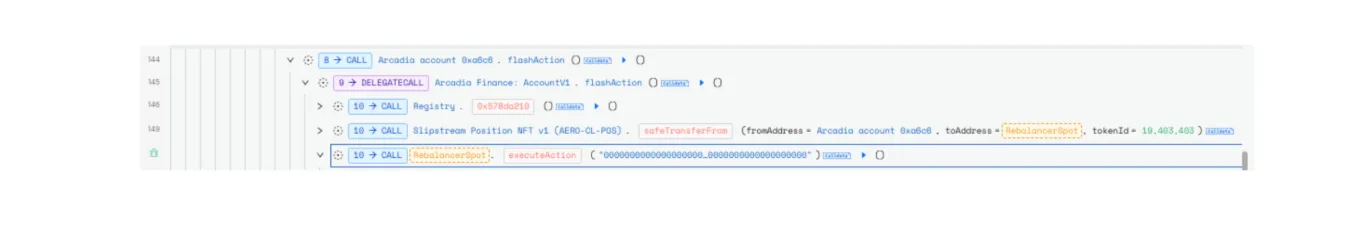
In this series of exploits, actionTarget is configured to be RebalanceSpot for reentrancy while router target the victim account and execution of data by the rebalancer drains the victim account.
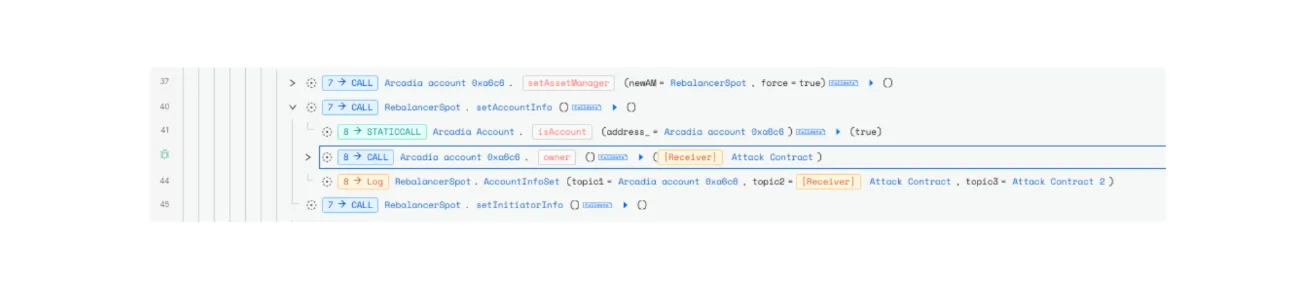
Set the AssetManager of the account 0xa6c6 to be RebalancerSpot and set the attack contract to be the account owner through RebalancerSpot.
Mint an LP NFT with 1,773 USDC and 0.123 Coinbase WBTC, then deposit LP NFT along with 10 USDC and 1 Coinbase WBTC into Arcadia Finance, as a pretense to the real action.
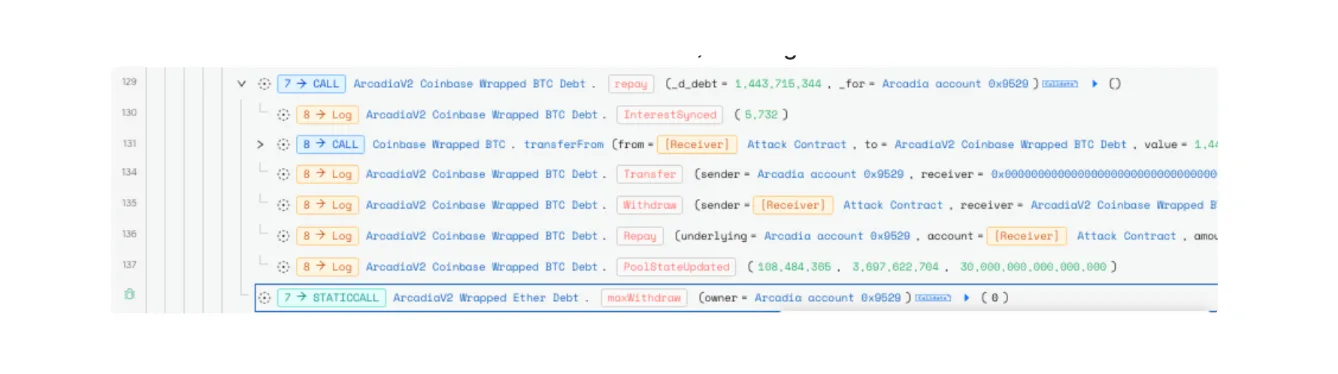
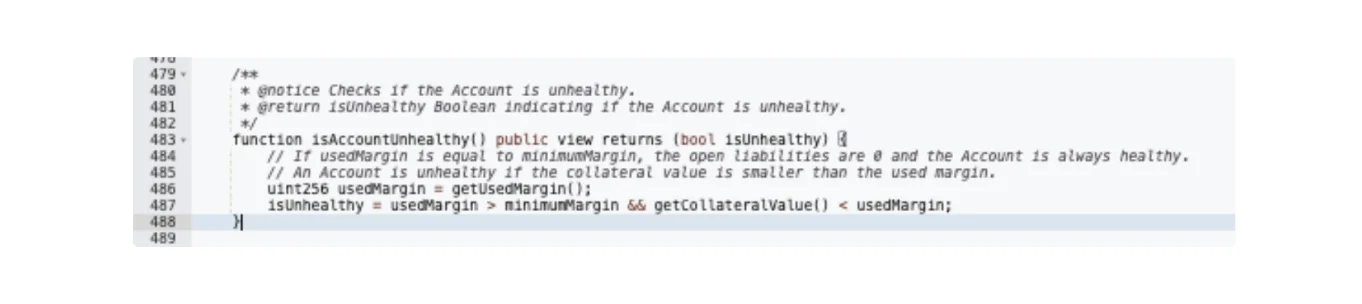
Repay 14.4 WBTC ArcadiaV2 Coinbase Wrapped BTC Debt on behalf of account 0x9529e5988ced568898566782e88012cf11c3ec99, the target victim account.
The repayment cleared the victim’s existing debt and will help to pass a health check in the AccountV1 contract after the theft.
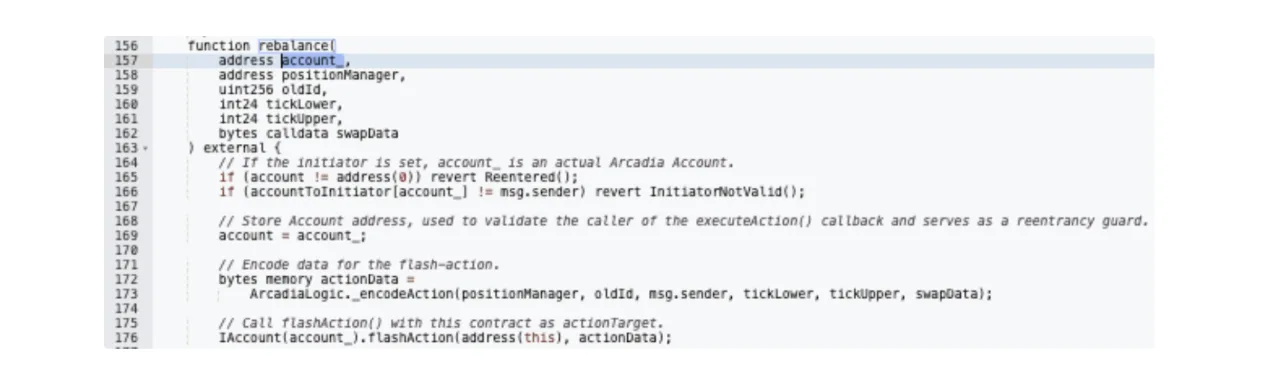
Call RebalancerSpot.Rebalance(), with arbitrary swapData.
When calling rebalance(), the input account_ is set to 0xa6c64642b546026c768d3c20ab9d2bcbbad88712 (1 of 15 exploiter-deployed dummy accounts). During the rebalance() function, ‘actionData’ is executed.
In this function, there is insufficient validation of either actionTarget and actionTargetData.
The exploiter is thus able to re-enter RebalanceSpot to execute the real operation.
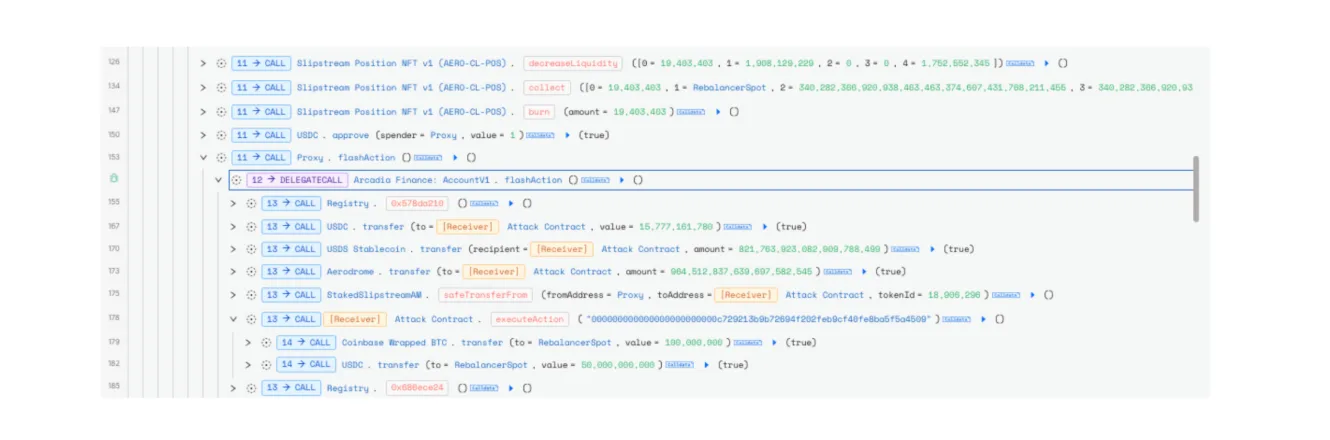
They first removed LP and withdrew 1,773 USDC and 0.123 Coinbase WBTC to RebalancerSpot.
The rebalance.executeAction() executed SwapLogic._swap() which, in turn, called SwapLogic_swapRouter().
This’ router’ hidden deep in the initial swapData is decoded to be the target victim, account 0x9529.
And from it, flashAction() is executed where 15.7K USDC, 821 USDS Stablecoin, 964 Aerodrome, and the LP NFT StakedSlipstreamAM (id = 18906296) were transferred to the attacker.
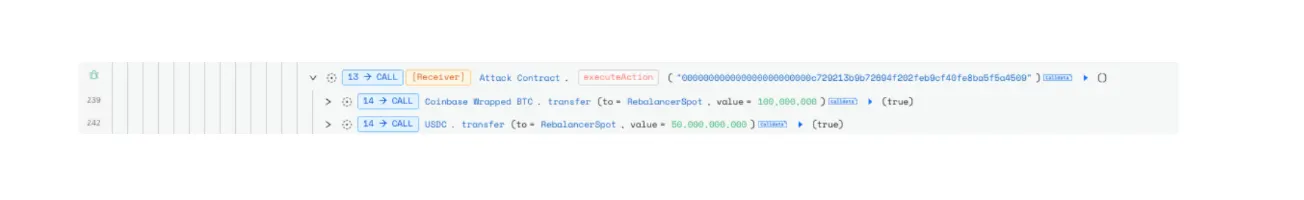
Finally, the exploiter donated to RebalancerSpot 50K USDC and 1 Coinbase WBTC
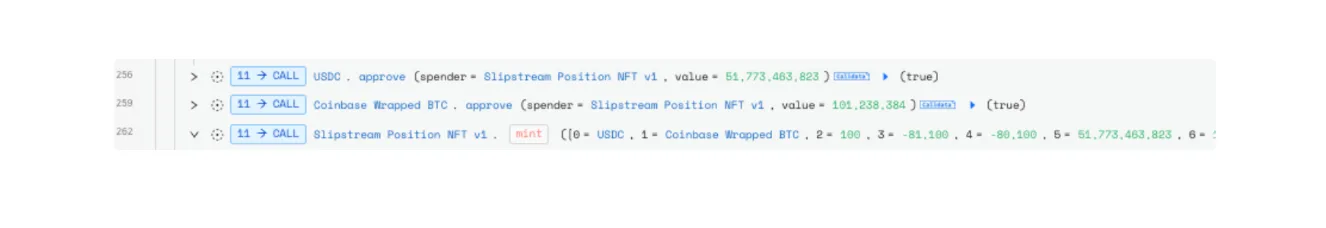
which was used to mint a Slipstream Position NFT v1
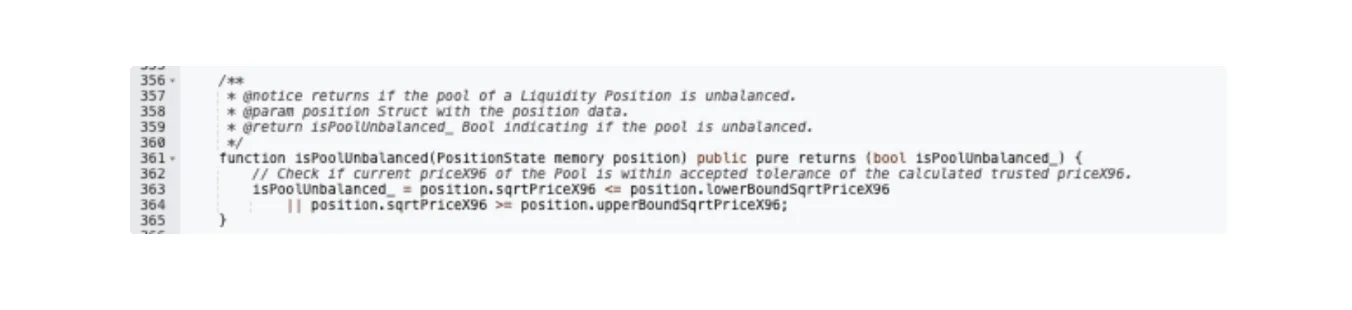
as is needed to ensure the Pool was balanced
Withdraw the Slipstream Position NFT v1 (AERO-CL-POS) along with the remaining tokens.
Remove the liquidity of LPs acquired, then repay flashloan.
Fund Flow
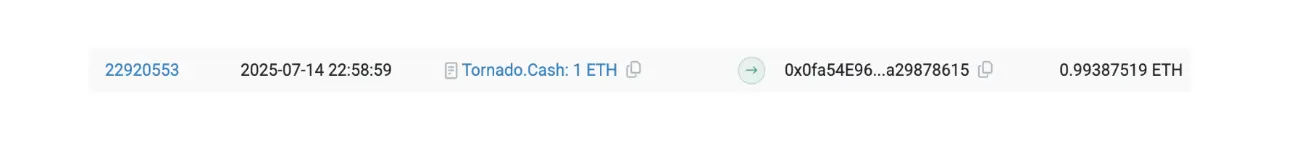
The exploiter’s wallet was funded by a Tornado Cash deposit 8 hours before the attack.
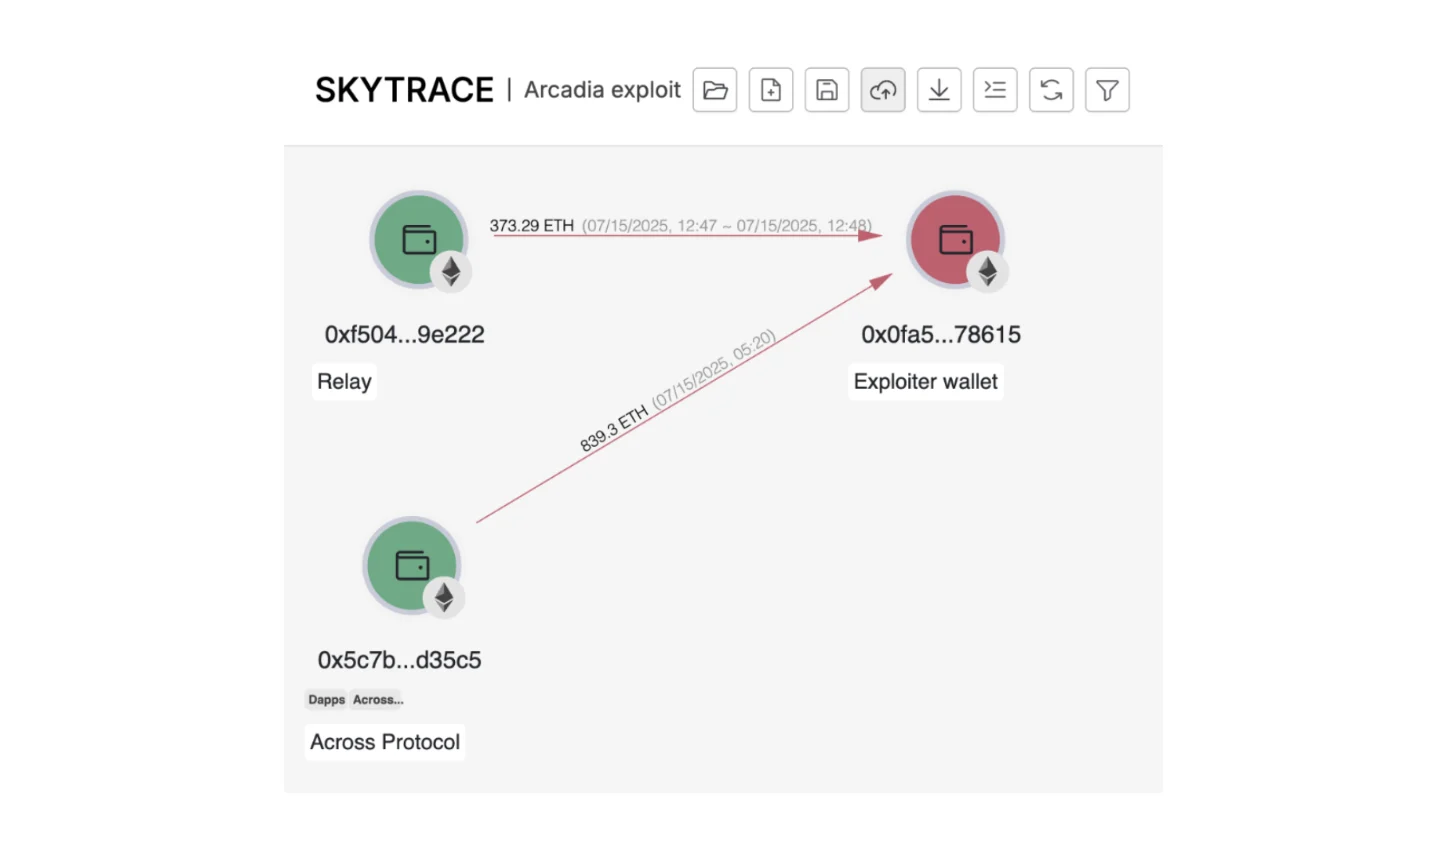
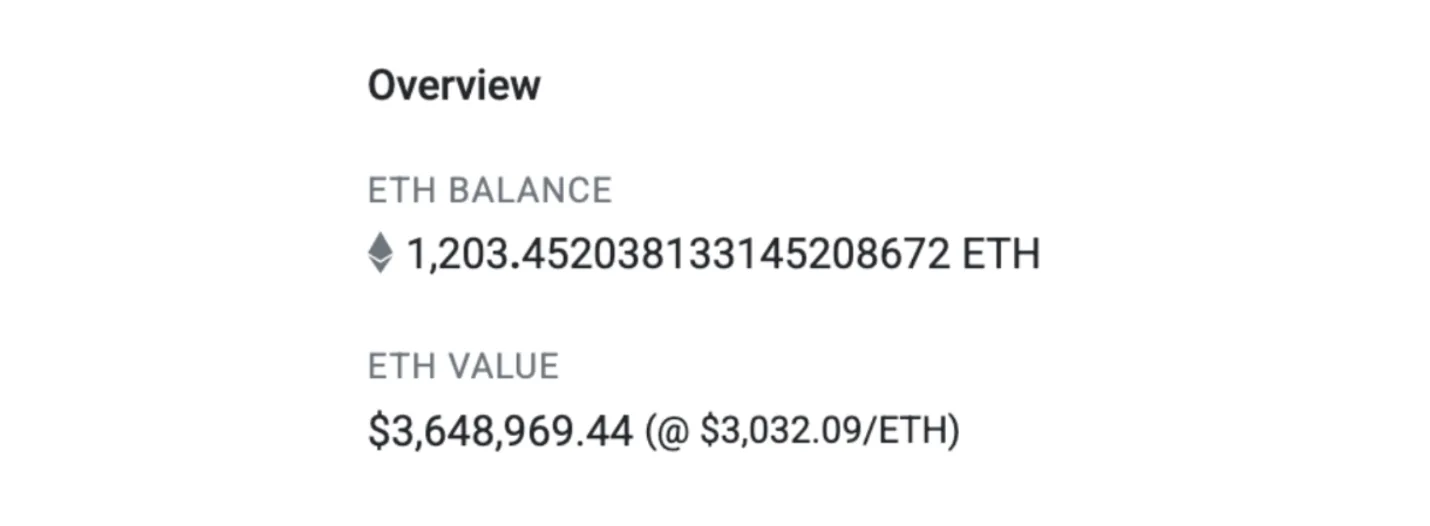
The exploiter swapped stolen funds for 1,203 ETH (~$3,6M) in 1inch, then bridged (opens in a new tab) the funds from Base to Ethereum network via Across Protocol and Relay.
As of writing the stolen funds are held in wallet 0x0fa5 on Ethereum.
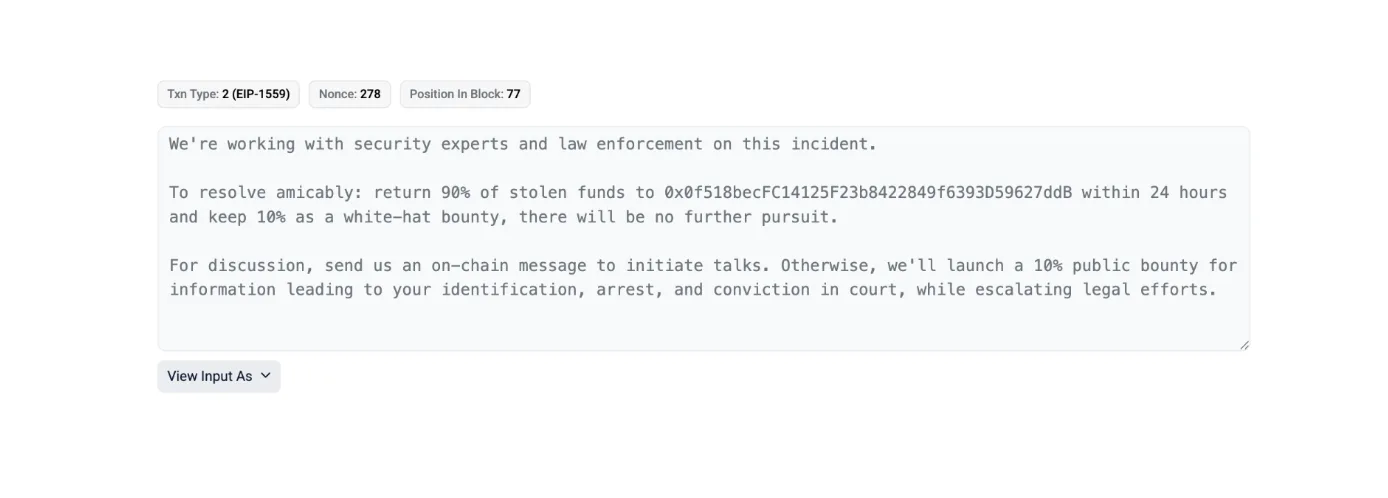
The Arcadia team has reached out to the exploiter to offer a 10% bounty for the return of the remaining funds.