Project name: Hashflow
Project type: DEX
Date of exploit: June 14th, 2023
Asset loss: $640,000
Vulnerability: Lack of Access Control
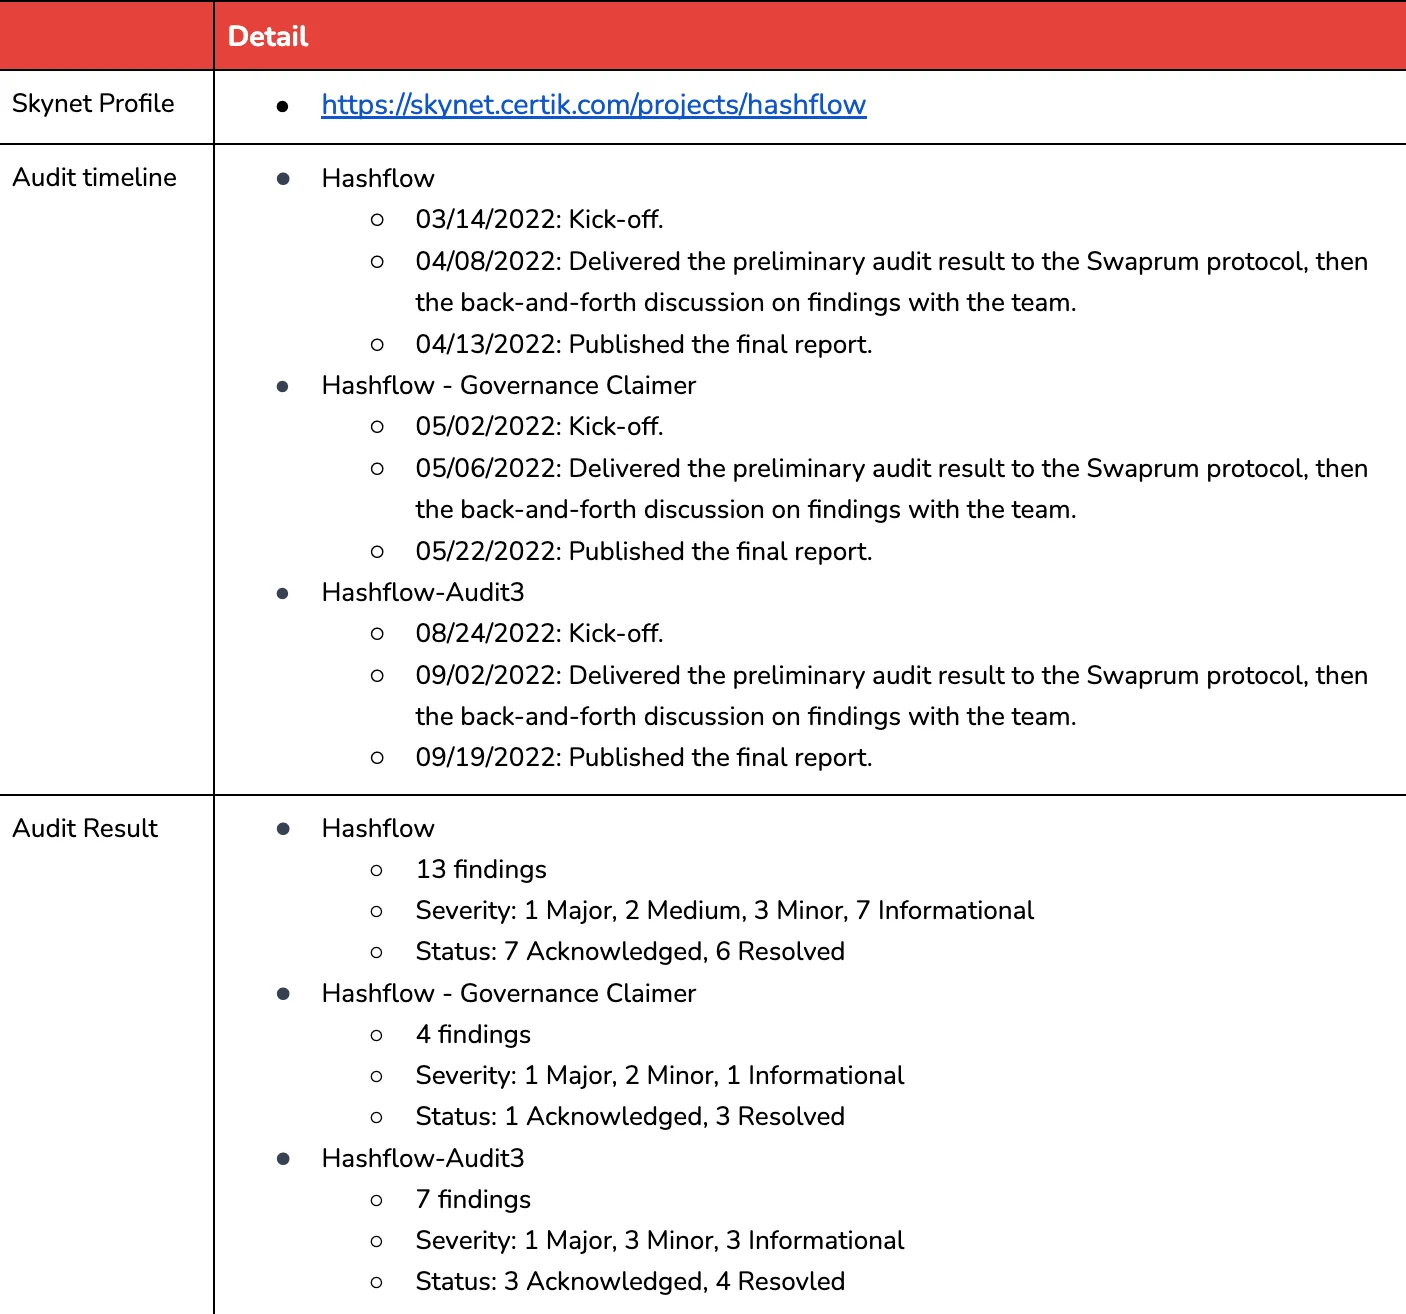
Date of audit report publishing:
- April 13th, 2022: Hashflow
- May 22nd, 2022: Hashflow - Governance Claimer
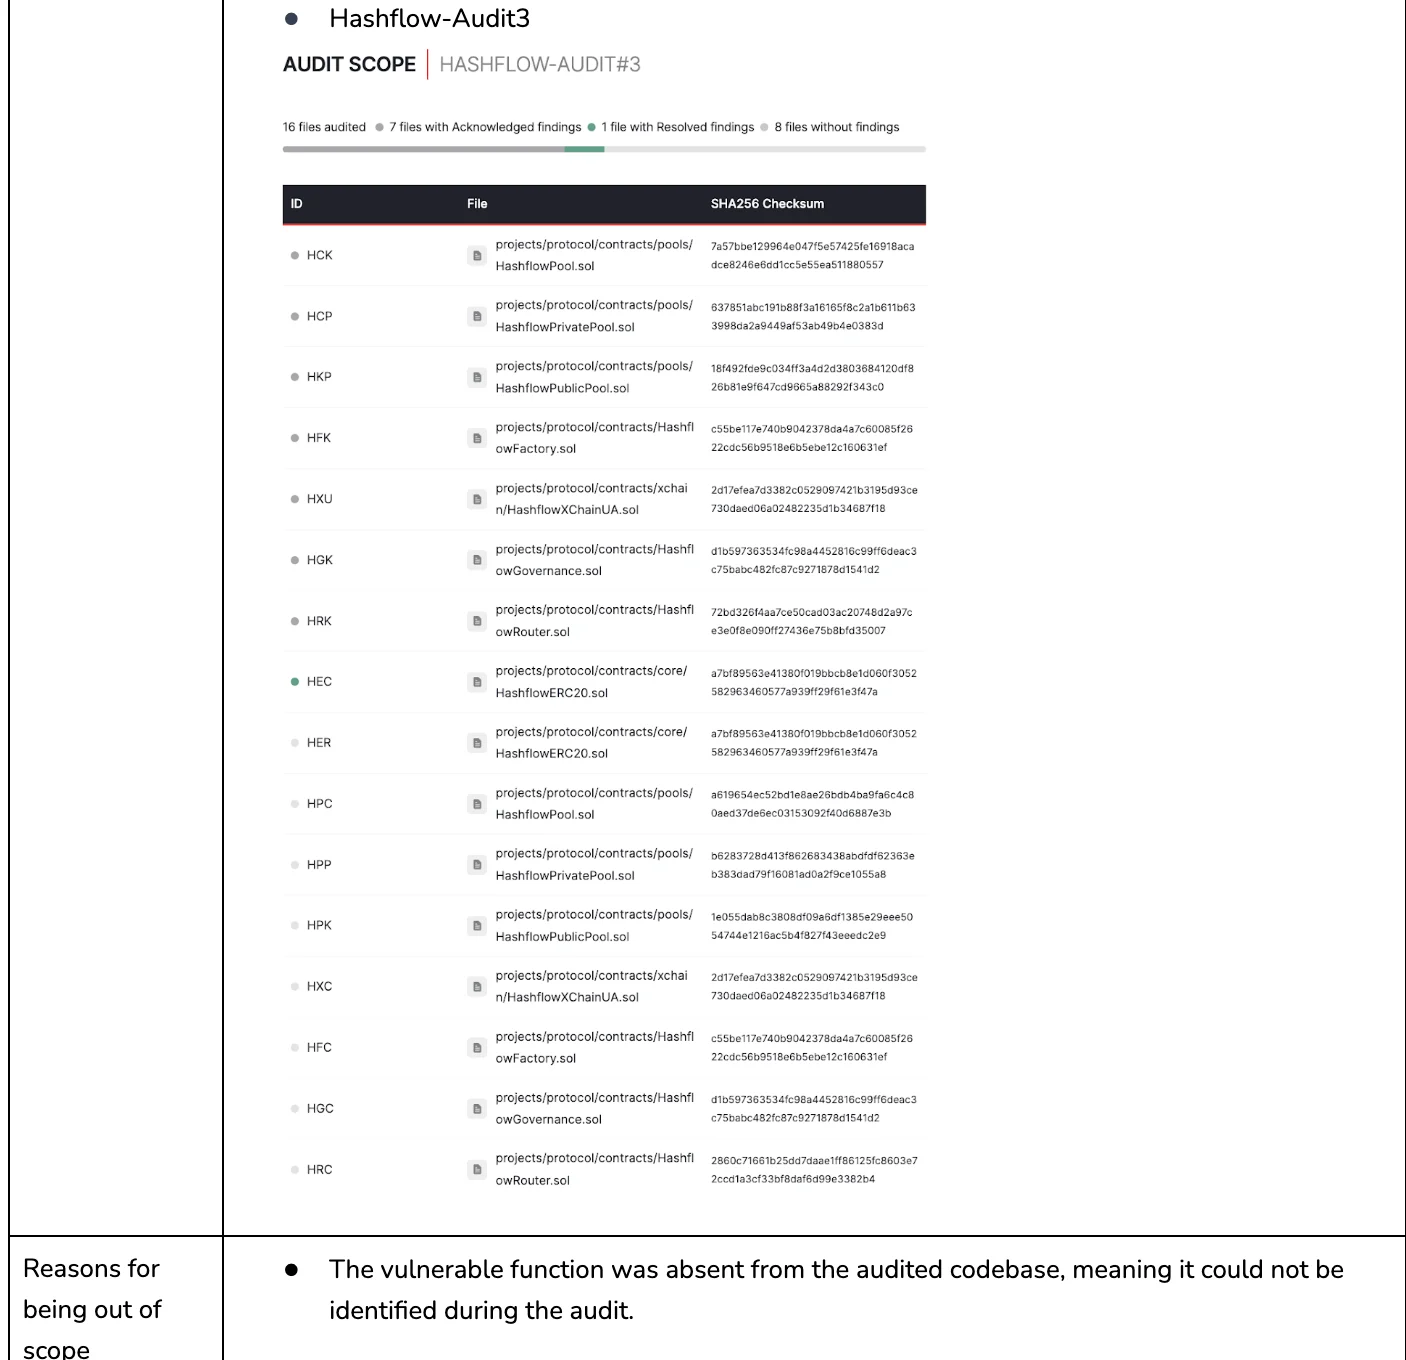
- Sep 19th, 2022: Hashflow-Audit3
Conclusion: Out of Audit Scope
Details of the Exploit
Background
Hashflow is a multichain decentralized exchange (DEX) that enables users to trade assets.
Nature of the Vulnerability
The vulnerable contract is unverified and the vulnerable 0x1ce5 function contains a transferFrom function the attacker could trigger to steal user funds when approved.
The attacker contract appears to have a recovery function that users can call to get their money back
CertiK Audit Overview
Conclusion
On June 14th, 2023, Hashflow experienced a loss of ~$605k across five chains. The vulnerable contract is unverified and the vulnerable 0x1ce5 function contains a transferFrom function the attacker could trigger to steal user funds when approved.
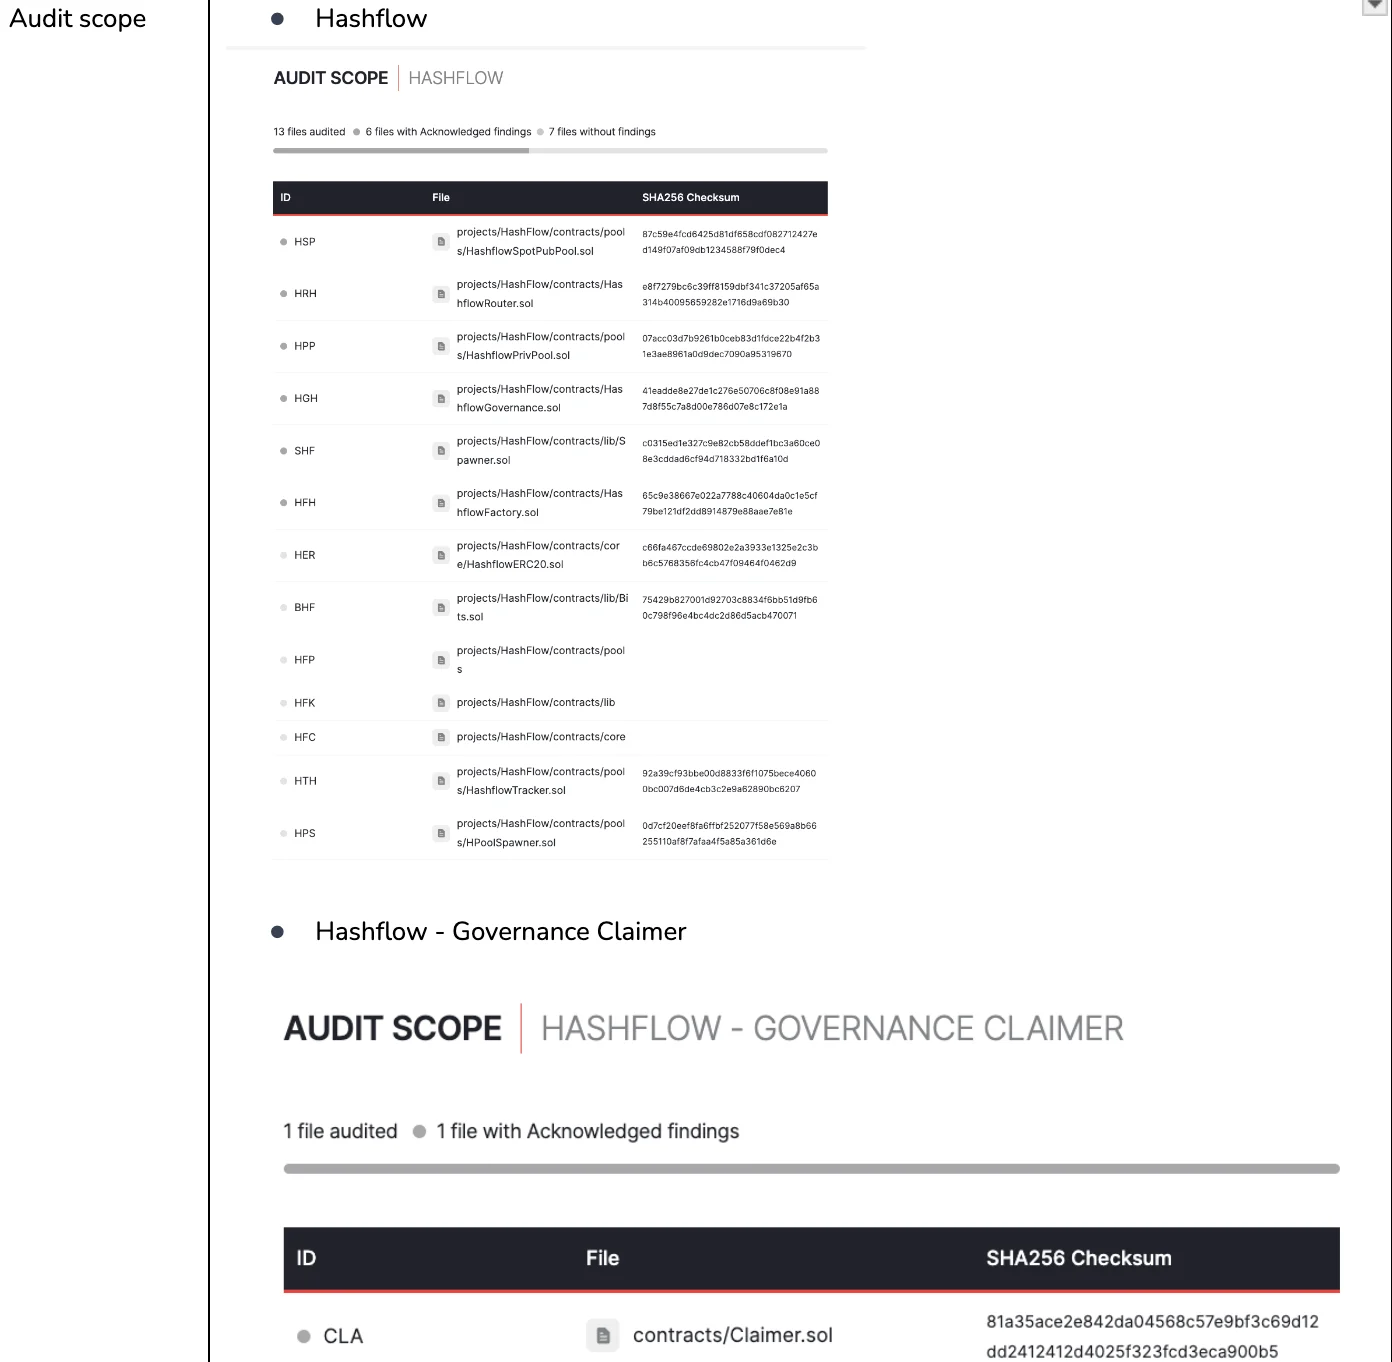
The vulnerable function was absent from the audited codebase, meaning it is out of the audit scope.